


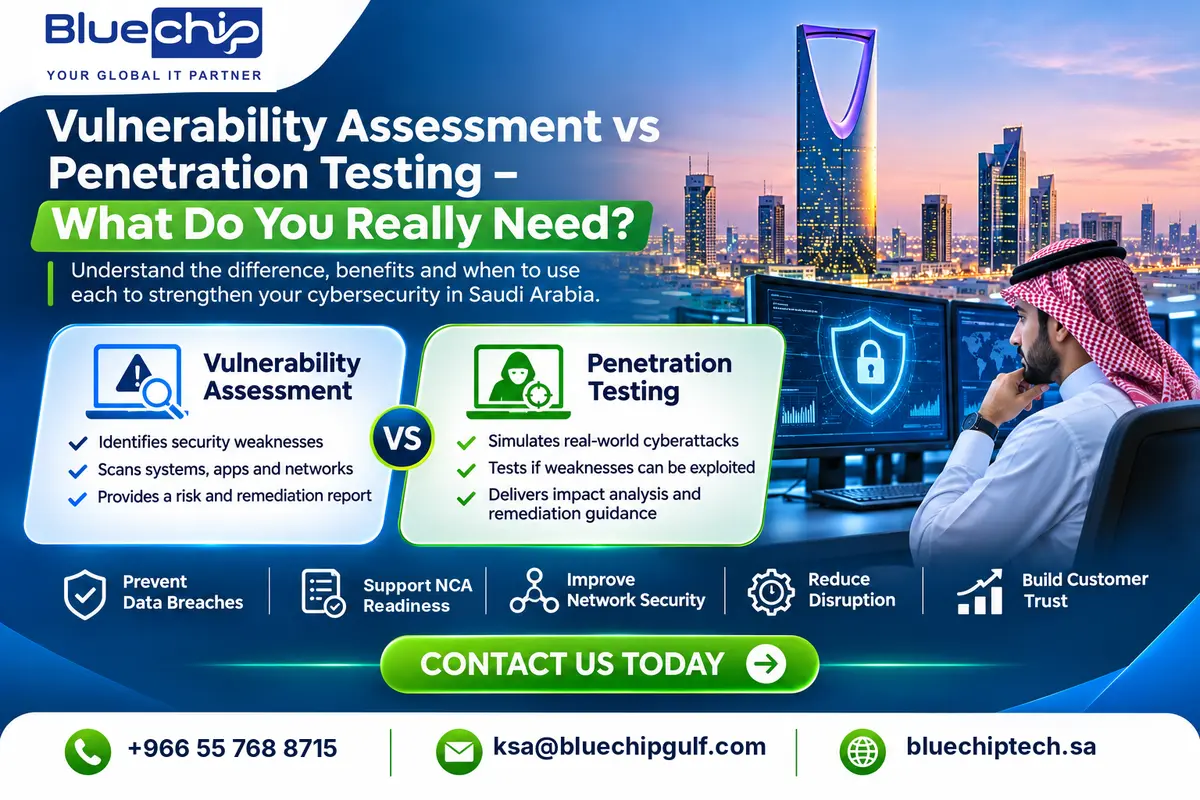
Vulnerability Assessment vs Penetration Testing – What do you really need?
Introduction
With an increasing number of businesses in Saudi Arabia embracing digitalisation, cybersecurity is now becoming more important than ever. Businesses can be in many different industries including finance, health, retail and government contractors, meaning they are holding increasing amounts of sensitive business and customer data.
However, whilst it may seem obvious that it is important to know what security issues exist within your organisation, it is also important to understand how they could be exploited. This is where Vulnerability Assessment and Penetration Testing can help.
Although often mentioned together, they are very different processes. By understanding the difference between the two processes, businesses in Saudi Arabia will be able to select the right penetration testing service for them.
1. What is a Vulnerability Assessment?
A Vulnerability Assessment is a process of identifying any security issues within your IT systems. This will help you understand where there could be issues within your systems so that they can be addressed before being exploited.
It will typically look at:
- Servers
- Computers
- Databases
- Websites
- Web Applications
- Mobile Applications
- Network Devices
- Firewalls
- Cloud Infrastructure
- Internal Networks
- Out of date Software and Configurations
For example, any out of date plugins on their website or misconfigured server that a retail business in Saudi Arabia may have can all be identified with a Vulnerability Assessment. The IT team can then prioritise the security issues they need to address.
The main goal is to help find any risks that may exist, analyse them and provide recommendations to help solve them.
2. What is Penetration Testing?
Penetration Testing takes the process of assessing your cybersecurity further. This is done by simulating an attack on your systems by security professionals to see if they can be exploited.
A professional penetration testing service will help you understand how an attacker could gain unauthorised access to your systems, applications and sensitive data.
For example, if there are any issues found during a Vulnerability Assessment with your login system, a Penetration Test will show if they can be exploited.
This helps organisations understand the true impact of security issues.
3. What are the Differences?
Whilst both aim to improve your cybersecurity, there are differences between the Vulnerability Assessment and Penetration Testing.
| Comparison | Vulnerability Assessment | Penetration Testing |
| Main purpose | Identify security weaknesses | Test whether weaknesses can be exploited |
| Approach | Scanning and analysis | Simulated cyberattacks |
| Testing method | Automated and manual checks | Manual and automated techniques |
| Risk identification | Highlights potential vulnerabilities | Demonstrates real-world security risks |
| Frequency | Regular assessments | Periodic and after major changes |
| Outcome | Vulnerability report | Exploitation findings and remediation guidance |
| Business value | Helps prevent security issues | Evaluates the effectiveness of existing defences |
Both tests compliment each other. Vulnerability Assessments will help find weaknesses and Penetration Testing will help understand how they could be exploited.
4. Why do Businesses in Saudi Arabia need them?
With an increasingly digital economy in Saudi Arabia, it is important to ensure that your business systems, applications and sensitive data are protected.
Many industries including banking, health, retail, manufacturing and government now rely on digital systems.
There are 5 reasons why businesses should consider undertaking both.
1. Prevent Data Breaches
Regular assessments will help highlight any weaknesses that could put your customers’ confidential data, financial data and internal data at risk.
2. Regulations
The National Cybersecurity Authority (NCA) have created Essential Cybersecurity Controls to help improve cybersecurity within national entities. These controls include those around Vulnerability Assessment and Penetration Testing. You should make sure to understand what applies to your organisation.
3. Improve Network Security
If you are using cloud based systems, remote access and have networked systems, regularly getting assessed will help highlight possible vulnerabilities.
4. Reduce Disruption
By identifying and addressing any vulnerabilities, there is less chance of cyber attacks, unexpected disruptions and financial loss.
5. Customer Confidence
Customers expect you to protect their personal and financial data. By showing you have a proactive approach to cybersecurity, you can increase customer confidence.
5. Who should undertake Vulnerability Assessments and Penetration Testing?
VAPT can be very beneficial to any organisation that uses digital systems or handles sensitive data.
Examples include:
- Banking & Finance – Protect their financial systems, customer accounts and payment systems.
- Healthcare – Secure patients data, medical data and networked healthcare systems.
- Retail & E-commerce – Secure their online payment systems, customer data and shopping systems.
- Manufacturing – Identify any security issues within their networks.
- Government – Improve their digital systems.
- IT & Tech – Assess their applications, cloud systems, networks and critical business systems.
Small and Medium sized businesses can also benefit from regular assessments. Cybersecurity should not just be considered important for large businesses.
6. How to Choose the Right VAPT Testing Company in Saudi Arabia?
When choosing between different VAPT testing companies, you should look at what technical expertise they have.
- Qualified Security Experts – Look for a provider who have experienced Cybersecurity experts with relevant professional qualifications.
- Thorough Testing – They should be able to test your applications, networks, cloud systems and other systems.
- Automation and Manual Testing – A mixture of both will help highlight common vulnerabilities and more complex issues.
- Detailed Reports – The provider should provide clear reports on what vulnerabilities were identified, how severe they are and recommendations.
- Experience – Choose a provider who have experience within different industries.
- Remediation – They should provide guidance on how to fix the issues identified.
This can help organisations in Saudi Arabia identify the best penetration testing companies.
7. How Bluechip Tech can Help Businesses in Saudi Arabia Improve their Cybersecurity
Understanding security issues is the first step to creating a better IT environment. We offer Vulnerability Assessment and Penetration Testing services so that you can identify and assess any potential security risks within your business.
Using automation and manual testing we can test your applications, networks and business processes. We will also focus on helping identify any critical issues and review possible risks whilst also minimising any false positives.
Our detailed reports will help you understand the issues that exist within your business.
Whether you require a Vulnerability Assessment in Saudi Arabia or a complete Penetration Testing service, it is important to chose the correct cybersecurity approach.
FAQs
What is the difference between a Vulnerability Assessment and a Penetration Test?
A Vulnerability Assessment will provide an organised method of identifying and classifying vulnerabilities within an agreed scope. A penetration test will attempt to exploit vulnerabilities in a controlled way showing how they could be exploited. They both ask different questions.
Would we benefit from doing both a Vulnerability Assessment and a Penetration Test?
Many organisations benefit from carrying out both. Vulnerability Assessments can be carried out more regularly to give general exposure, whilst Penetration Tests will give more detailed validation. Which option to choose will depend on your risk, criticality of systems, any changes to your environment, customers requirements and any regulatory or contractual requirements.
How often should I carry out a Penetration Test?
There is no one size fits all answer. Any testing should be based around any regulatory or contractual requirements and risk. It is common practice to carry out a penetration test after any major changes to applications/infrastructure, prior to major launches, after any major security incidents or after a set period of time. If you have internet facing systems or high risk systems you may want to carry out more regular assurance than if you have low risk internal systems.
What should I look for when choosing a Penetration Testing company for my business in Saudi Arabia?
Firstly you should decide what the scope of testing will be. Then check the methodology they will use, experience of testers, terms of engagement, how they will handle data, quality of evidence, reporting, retesting, ability to communicate how it affects your business and what to remediate first. Ensure they will not cause unnecessary disruption. If there are any Saudi licensing or regulatory requirements for the Cyber Security service ensure these are met and that the company has the relevant status with the correct authority.


